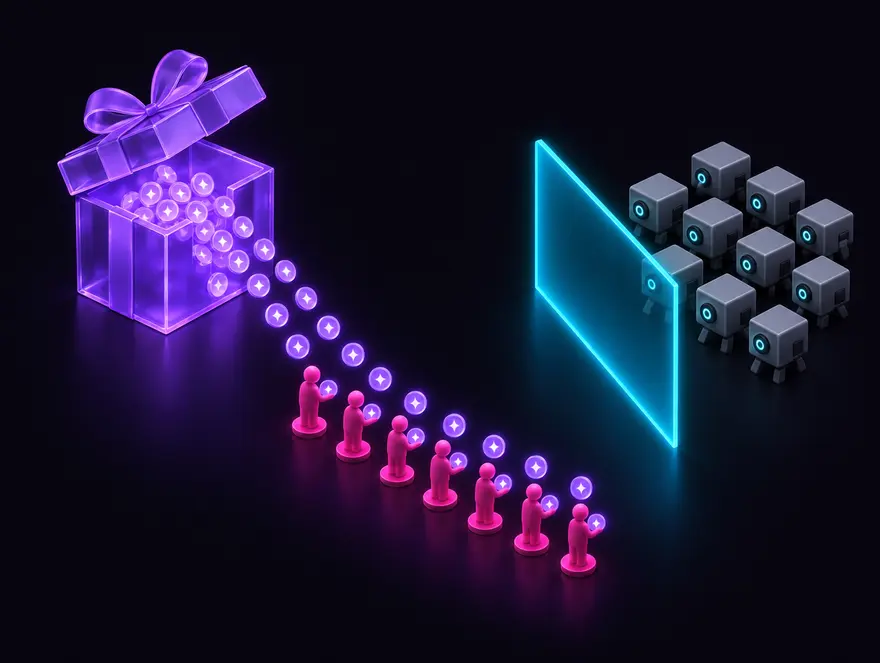
Airdrops & rewards
Pay each person once. Fifty wallets on one phone still get one claim.
Xodian lets your app confirm that each user is one real human on a genuine phone. No selfies, no ID uploads, no personal data. Your app gets a signed, private credential, and each phone can produce only one per app.
Why it matters
A farmer with fifty wallets looks like fifty users to you. Xodian ties each answer to the hardware key in one genuine phone, so the farm becomes one claimant again.
Every wallet counts as a person. One phone farm drains the campaign.
Same phone, same person, same sub. The other 49 wallets resolve to one ID.
Illustration of the rule, not a measurement: Xodian returns the same pairwise ID for every wallet on one phone.
Built for
Pay each person once. Fifty wallets on one phone still get one claim.
One account per player for ranked play, trials and starter bonuses.
One person, one vote, without asking members who they are.
Filter bots before KYC, so you only pay for full checks on real people.
How it works
They scan, read what's shared, and confirm in omni. Your backend gets a credential it can verify offline.
Acme Airdrop wants to confirm you're a real person
Acme Airdrop now knows you're a real person, and nothing else.
◆ EstablishedPrivacy by construction
Your users keep their privacy, and you don't take on the liability of storing data you never needed.
{
  "iss": "https://xodian.xode.net",
  "aud": "rp_acme",
  "sub": "oid_9f3c1a…e07b",   // only you see this
  "human": true,
  "level": 2,
  "level_name": "established",
  "uniqueness": "new",
  "nonce": "claim-8812",
  "receipt": "1759651200-a1b2c3d4"
}
Assurance
Set minLevel when you open a session. Below it you get rejected and nothing else, and omni tells the person privately how to qualify.
The phone signs with a key that cannot leave its secure chip, so a copied wallet seed is not enough.
Google and Apple vouch that the device and the app are genuine and unmodified.
A different ID for every app, so partners can't join their data to track a person.
Every decision is anchored on XODE hourly, so anyone can check it wasn't changed afterwards.
Integrate
It's plain HTTPS and a standard JWT, so any language and any JOSE library will work.
Sandbox
Test keys work like live keys, except a simulator answers instead of a phone. Tokens verify with the same code and carry "test": true. Reject that flag in production.
Free and instant. You can get up to 5 keys a day, and each key allows 500 sessions a day.
This is the only time the secret is shown. Store it before you leave the page.
The session opens with your key. Then choose how the "phone" answers.
// Get a test key to begin. Every call you make appears here,
// with the exact request your server would send.
Live demo
This runs against the production service. On the right is exactly what a partner's backend receives.
Open omni on your phone, then scan the code. On mobile, the button opens omni directly.
// Waiting. Press "Verify with Xodian" to start.
API reference
Base URL is https://xodian.xode.net. Authenticate server calls with Authorization: Bearer osk_….
| Endpoint | Auth | Purpose |
|---|---|---|
POST/v1/sessions | secret | Body {scope, minLevel, reference}. Returns sessionId, url, deeplink, pollToken and expiresAt (5 min). |
GET/v1/sessions/{id} | secret | Status. Once approved, also idToken, sub and level. |
GET/v1/sessions/{id}/status?t= | pollToken | Status only, safe to call from the browser. The widget uses this. |
POST/v1/test/clients | none | Self-serve sandbox key: {name} → client id and secret. |
POST/v1/test/sessions/{id}/simulate | test session | Answer a test session: approve, deny, reject or expire. |
GET/v1/.well-known/jwks.json | public | Signing keys (ES256, selected by kid). |
GET/sentinel/receipt/{receipt} | public | Merkle proof that the decision was anchored on the XODE chain. |
pending → approved | denied | rejected | expired. Each session can be used once.
session.* and grant.revoked events, signed with X-Omni-Signature: t=…,v1=HMAC_SHA256(secret, t.body).
Verify the signature, then iss, aud, exp, and that nonce equals your reference. Use sub as the user key.
new, returning (same person or same phone), or contested (this wallet moved onto a phone already used by someone else). Treat contested as a likely duplicate.
Questions
No. Xodian proves that someone is one real person on a genuine phone. It never learns or shares who they are. Many teams use it before KYC, so they only pay for full identity checks on people who pass.
No. There are no selfies, no face scans and no ID uploads. The proof comes from the phone's hardware key and from Google Play Integrity or Apple App Attest.
They keep the same ID for your app, because the wallet carries it across. A wallet that moves onto a phone already used by someone else comes back marked contested, so you can decide how to treat it.
Yes, one ID per genuine phone. Level 2 makes that expensive, because each phone has to be kept active for weeks. What Xodian removes is the cheap version: many wallets, emulators and modified apps on one device.
Xodian is in early access for partners building on XODE. Test keys are free. For live keys and pricing, contact us.
Get a test key in seconds and finish your integration today. For live keys, tell us what you're protecting.